Enterprise device management,
end to end
Built for corporate IT, phone rental, instalment sales and work phones — supervision, remote lock, device location and e-contracts, from issue to retirement.
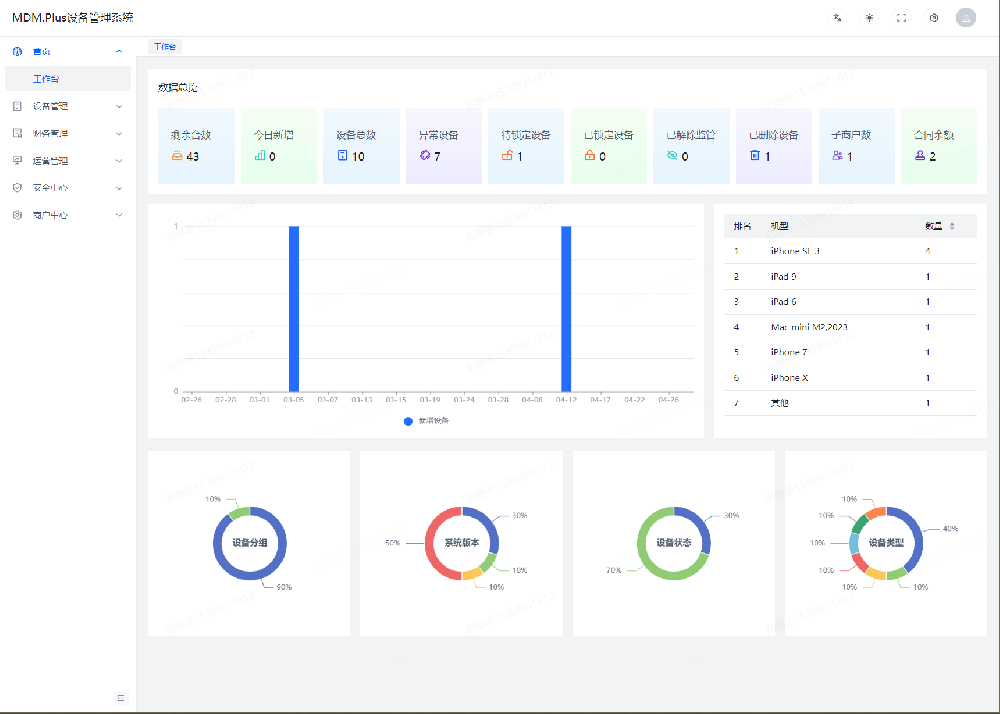
Six core capabilities
Each one maps to a concrete action in daily operations.
Feature Restrictions
All policies can be customized, including: Disable Erase; Disable Installation of Configuration Profiles; Disable Enterprise Apps; Disable Conne···
App Policies
Can remotely install and uninstall apps from the AppStore, and can also remotely install and uninstall third-party enterprise apps; can view the···
Configuration file management
You can obtain, delete installed description files and independently manage individual policy projects.
Equipment positioning
The device can be located independently when the lock is successful, or the lock and locate function can be used to automatically locate the dev···
Card insertion record
You can view the current card insertion information and historical card insertion records.
Real-time active area
You can view the current active area of the device without locking it.
Everywhere you work
Desktop, mobile and utility tools share the same data.
Four lines, one platform
Who receives the device and what it is used for decides the policy.
Corporate IT
Company-issued phones and tablets enrolled automatically, with department policies, compliance status and remote recovery at offboarding.
Hire to exitPhone rental
Enrolled at signing and bound to the customer, order and contract. Overdue escalates in stages; return wipes and releases for re-lease.
Full lifecycleInstalment
Device tied to the payment plan with reminders, a collection mode restricting apps and network, and remote lock when needed.
Payment linkedWork phones
Purpose-built devices with OPPO, with controls pre-installed. Within an authorised scope, work-related calls, SMS and WeChat can be retained and audited; remote lock and wipe on loss or exit.
Custom device · OPPORetention of communication content requires company-owned devices, written notice and employee authorisation, limited to work purposes. Features and delivery are subject to the agreed product description and service agreement.
Notes from the returns desk
Most odd device behaviour is a policy firing as designed, not a fault.
A charging icon does not mean charging
Real wireless power depends on alignment, negotiated tier and battery temperature. Since iPhone 12 only certified magnetic pads reach 15W; generic pads cap at 7.5W.
Read → SecurityLocked for an hour, the data port closes
USB Restricted Mode since iOS 11.4.1 cuts data enumeration after an hour locked, keeping charging only. Supervised devices can be granted an exception by profile.
Read → ConfigThe VPN you cannot delete is not the one you added
A management-pushed VPN is part of a configuration profile and cannot be removed by the user. Telling policy from fault saves hours.
Read →Latest articles
OS updates, vulnerabilities and device mechanics decide whether control still works.
MDM 26.11.17: Managed App Tab and Employee Operation Quotas
→MDM 26.11.12: Auto-Install Managed App via Device Model Policy
→MDM 26.11.11: Agent Employee Accounts and Google Token Access
→MDM 26.10.26: Random Unlock PIN, Uninstall Alerts, and Batch Locking
→MDM 26.8.21: Anti-Bypass Lock Mode for Apple Devices
→MDM V26.8.14: Unified Electronic Contract Entry Across MDM, WeChat Mini Program and Alipay Mini Program
→Frequently asked
Which devices are supported?
iPhone, iPad, Mac and Android phones and tablets. iOS uses Apple Business Manager and ADE supervision; Android uses Android Enterprise. Both are vendor frameworks — no jailbreak, no third-party plugins.
Does it require jailbreaking?
No. Every capability is built on vendor-published frameworks, so policies keep working after OS updates.
How are overdue devices handled?
In stages: reminder, then restricted apps and network, then remote lock, and finally location confirmation, wipe and supervision removal so the device returns to inventory.
How are devices recovered when staff leave?
Issue a remote wipe and supervision removal from the console. The device executes it once it reconnects; no physical access needed.
Is on-premise deployment available?
Yes. Deploy on your own servers or private cloud. Data stays inside your network, with integration for directories, SSO and internal systems.
Can work phones be audited for calls and WeChat?
On purpose-built devices made with OPPO, work-related calls, SMS and WeChat can be retained and audited within an authorised scope — requiring company-owned devices, written notice and employee consent, limited to work purposes.
Talk to a person
Tell us the fleet size, device mix and scenario. You get a straight answer.